


कोट-पुष्टि। स्कोप-लॉक। कोई छिपा हुआ नियम नहीं।
प्रत्येक जुड़ाव एक लिखित प्राधिकरण पर आधारित होता है। डेटाबेस लेयर पर सीमाएं लागू की जाती हैं।
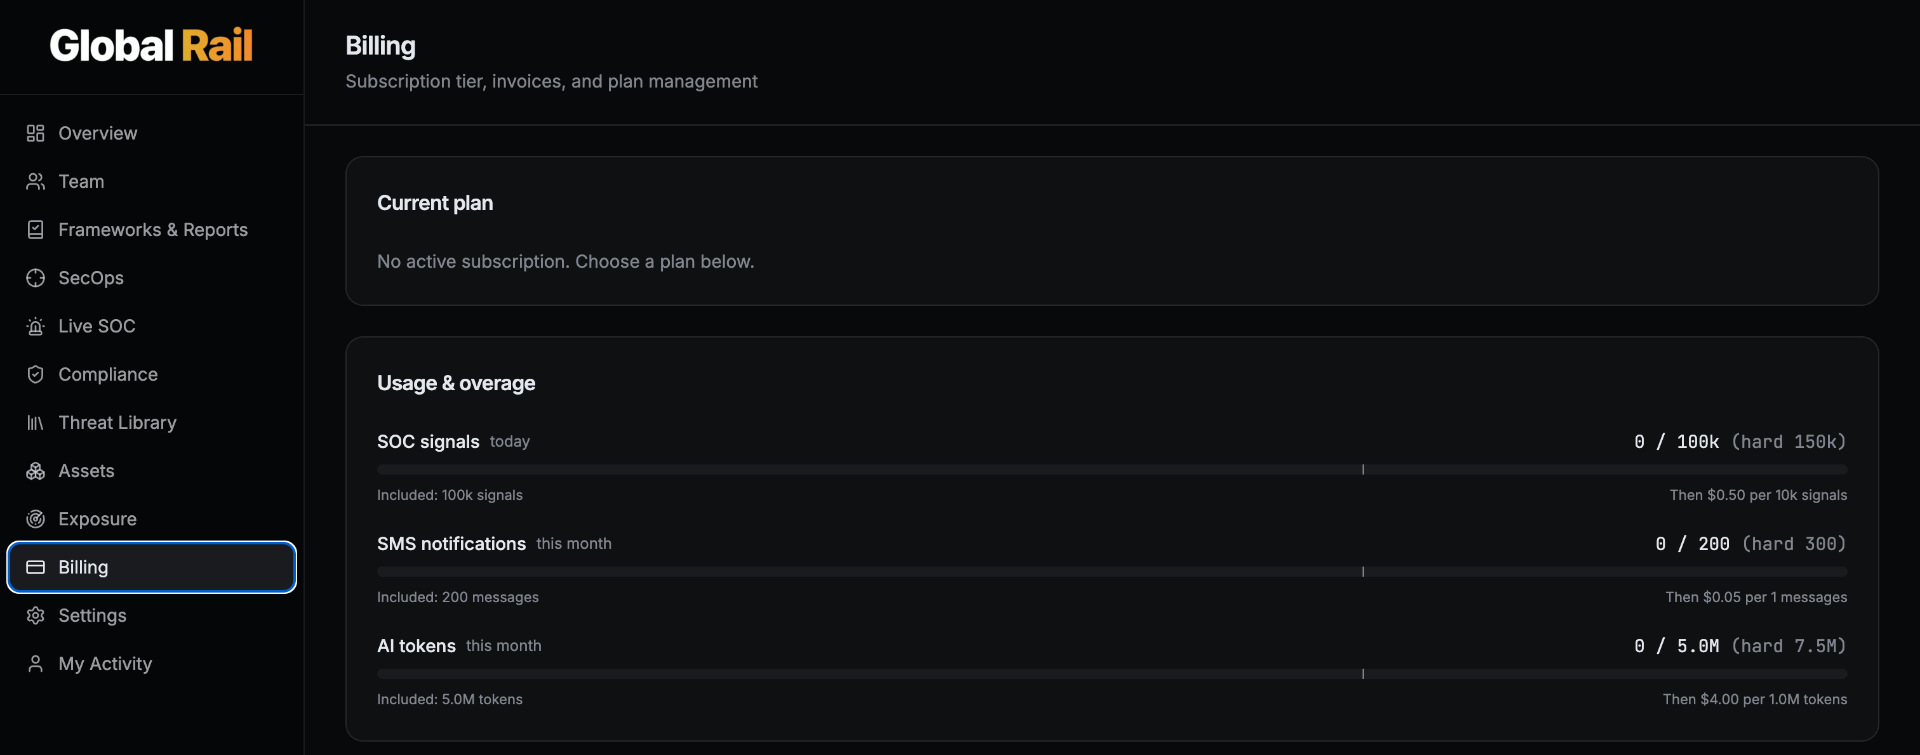
देखें कि आप वास्तव में क्या उपयोग करते हैं।
सब्सक्रिप्शन टियर, इनवॉइस और प्लान मैनेजमेंट एक ही स्थान पर — SOC संकेतों, SMS सूचनाओं और AI टोकन के लिए लाइव मीटर के साथ। सॉफ्ट कैप्स आपको चेतावनी देते हैं; हार्ड कैप्स आपकी रक्षा करते हैं।
तीन प्लान्स। सभी कोट-पुष्ट।
कस्टम और प्रति-ऑडिट स्कोपिंग उपलब्ध है — हर अनुबंध एक लिखित प्राधिकरण से जुड़ा होता है।
प्रत्येक प्लान पर 7-दिन का फ्री ट्रायल · कार्ड आवश्यक · 7 दिनों तक कोई शुल्क नहीं · कभी भी रद्द करें
हर कमिट को स्वायत्त सुरक्षा जाँच मिलती है — केवल सिद्ध निष्कर्ष, कोड के रिव्यू या प्रोडक्शन तक पहुँचने से पहले।
कार्ड आवश्यक · 7 दिनों तक कोई शुल्क नहीं · कभी भी रद्द करें
- 1 रिपॉजिटरी · हर push और pull request पर चलता है
- वेब ऐप्स, APIs, बैकएंड सेवाएँ और Web3/DeFi गणित को कवर करता है
- हर निष्कर्ष के साथ काम करने वाला PoC (कोई सैद्धांतिक अलर्ट नहीं)
- Slack + GitHub PR एनोटेशन, टिकट-रेडी
बाइनरी, वेब, क्रिप्टो और लाइव-LLM पर अनुसूचित स्टेजिंग-नेटवर्क एक्सप्लॉइट स्वीप्स।
कार्ड आवश्यक · 7 दिनों तक कोई शुल्क नहीं · कभी भी रद्द करें
- Web2, Web3 और AI-एजेंट सतह
- अनुमति सूची वाले स्टेजिंग लक्ष्य
- प्रति खोज कार्यरत एक्सप्लॉइट स्क्रिप्ट
- रीअल-टाइम PoC लॉग्स
फर्में ब्लाइंड इनिशियल पास को लाइसेंस देती हैं जो संकलित PoC उत्पन्न करते हैं — अब रीअल-टाइम हमले की पहचान के लिए Live SOC के साथ।
कार्ड आवश्यक · 7 दिनों तक कोई शुल्क नहीं · कभी भी रद्द करें
- सभी सतहें · मल्टी-इंगेजमेंट वर्कस्पेस
- AI नैरेटिव ड्राफ्टिंग
- मॉडल कॉल्स का पूर्ण ऑडिट ट्रेल
- कस्टम रेंज इंटीग्रेशन
- Live SOC: रीअल-टाइम SIEM/EDR इनजेस्ट + MITRE-टैग की गई घटनाएं
- अनुशंसित-और-बचाव प्लेबुक्स · email / Slack / Teams / PagerDuty
कस्टम और प्रति-ऑडिट स्कोपिंग उपलब्ध। सभी प्लान आपके लिखित प्राधिकरण के आधार पर स्कोप-लॉक्ड हैं।
Audit-grade pentests at a price designed to undercut the market.
One-off engagements priced $1 below the leading autonomous-pentest vendor — or bundled at no extra cost into any Range Assessment / Audit Co-Pilot contract over $2,000/month.
Pentests included on every contract over $2,000/month.
Annual contracts: pentests scheduled per release. Talk to sales for a custom cadence.
Comprehensive pentest for a single application.
Lightweight apps with few interconnected features, a modest set of CRUD resources, simple workflows, low integration complexity.
Equivalent depth of a 2-week manual penetration test.
- Compliance-ready report: SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, NIST CSF, NIS2, ISO 42001, TS 50701 + 40 more frameworks
- Audit-ready report within 5 business days
- Free re-test with automated verification after fix
- Frictionless authenticated testing (2FA, magic link, email)
- Detailed proof-of-concept exploits
- Actionable remediation guidance
- Black-box, white-box, or grey-box
- Every finding human-reviewed before it ships
Deeper coverage for more complex applications.
Apps or platforms with multiple modules, integrations, multi-step workflows, deeper access-control patterns and data models.
Equivalent depth of a 4-week manual penetration test.
- Everything in Single Target
- Authenticated multi-role testing across tenants
- Web2 + Web3 / smart-contract + AI-agent surface coverage
- IDOR, SSRF, deserialization, auth-bypass, prompt-injection, tool-abuse probes
- Realtime streaming of findings into your Console
- Vulnerability coverage map + reasoning trace per finding
- Request/response and endpoint-level trace detail
- Two free re-tests after fixes ship
Continuous coverage for organisations at scale.
Mature application portfolios — multi-module SaaS, admin tools, extensive resource relationships, regulated environments.
Continuous security hardening across every release.
- Everything in Full Surface
- Continuous offensive coverage — re-runs on every release
- Early access to new vulnerability coverage as we ship detections
- Multi-member access, shared assessment knowledge, human-directed operatives
- Single Sign-On (SSO) + API access for workflow integration
- Quarterly executive readout + framework-mapped board pack
- Dedicated detection-engineering channel for your stack
Prices are per application, per test. Re-tests after fix are free. Every finding is human-reviewed before it ships — we never push automated changes to your environment.
Single Target and Full Surface: submit scope, pay securely on the next step, work starts the same day.
7 दिनों के लिए नि:शुल्क। कार्ड आवश्यक है। 8वें दिन से पहले कभी भी रद्द करें।
- अपनी कंपनी के ईमेल से साइन अप करें और एक प्लान चुनें। हम पहले से ही एक मान्य भुगतान विधि एकत्र करते हैं, लेकिन 7 दिनों तक कुछ भी चार्ज नहीं किया जाता है।
- प्लेटफ़ॉर्म को एंड-टू-एंड चलाएं — एक लक्ष्य को अधिकृत करें, ऑडिट लॉन्च करें, C4 निष्कर्षों की समीक्षा करें, निर्यात करें framework-mapped रिपोर्टें। आपके प्लान द्वारा सीमाएं लागू।
- 8वें दिन आपके कार्ड से मासिक प्लान शुल्क लिया जाता है और आपकी सदस्यता प्रकाशित मूल्य पर महीने-दर-महीने जारी रहती है।
- कभी भी रद्द करें यहाँ से /billing → Manage (Stripe ग्राहक पोर्टल)। 8वें दिन से पहले रद्द करें और आपको कुछ भी भुगतान नहीं करना होगा।
बिलिंग को Stripe द्वारा पूर्ण कर, धोखाधड़ी और विवाद प्रबंधन के साथ संभाला जाता है। बैंक स्टेटमेंट दिखाते हैं LINK.COM* SMERT.AI। देखें शर्तेँ और गोपनीयता।
फाल्स पॉजिटिव्स का पीछा करना बंद करें।
प्रमाण भेजना शुरू करें।
हमें एक रेपो, एक कमिट, या एक अधिकृत स्टेजिंग लक्ष्य दें। हम संकलित, सफल एक्सप्लॉइट्स के साथ वापस आएंगे — अन्यथा कुछ नहीं।
ट्रायल के लिए कार्ड आवश्यक है। 7 दिनों तक कोई शुल्क नहीं। कभी भी रद्द करें।